Router security rarely gets the same attention phone and laptop security does, mostly because a router just sits in a closet doing its job silently for years at a time. 2026 has been a genuinely bad year for that assumption specifically: NETGEAR, TP-Link, Tenda, and D-Link have all disclosed real, model-specific vulnerabilities this year, ranging from medium-severity bugs to critical command-injection flaws, and checking whether a specific router model is on any of these lists takes less time than most people spend picking a Wi-Fi password.
NETGEAR’s August 2026 Advisory, By the Numbers
NETGEAR’s own August 2026 security advisory disclosed eight distinct CVEs across its router and mesh-system lineup, spanning a genuinely wide model range including the BE9300, several RAX-series routers, RS-series mesh units, and Orbi-branded MR/MS models. The most serious of the batch, two command-injection flaws (CVE-2026-11814 and CVE-2026-11739), are rated medium severity and allow a network-adjacent attacker able to intercept and modify local network traffic to compromise the router’s confidentiality and integrity. A separate pair of input-validation flaws (CVE-2026-11737 and CVE-2026-11738) let an authenticated administrator on the local network make unauthorized changes to device software and functionality. NETGEAR has published specific fixed firmware versions for every affected model, ranging from V1.0.1.84 up through V1.2.14.114 depending on the exact device, meaning the fix already exists; it just requires actually installing it.
TP-Link’s Hardcoded Credential Problem
TP-Link’s CVE-2026-12001 is a different category of flaw entirely: hardcoded authentication credentials embedded directly inside the firmware image itself, recoverable through firmware analysis and usable to gain unauthorized access to privileged router functions. It carries a CVSS v4.0 score of 5.2, medium severity, and affects five specific models: the TL-WR845N (V4), TL-WR850N (V3), TL-WR902AC (V4), Archer C20 (V6), and Archer MR200 (V5). Worth noting specifically: three of those five models are region-specific and not sold in the US, so a US-based reader checking this list should focus on the Archer C20 and TL-WR902AC specifically. TP-Link has released patched firmware for all five affected models regardless of region.
The More Serious Problem: Tenda and D-Link
The Tenda and D-Link disclosures are a meaningfully more serious category. Tenda’s AC21, TX9, and TX3 models carry five separate CVEs, several rated high severity, covering buffer overflow flaws in MAC filtering, Wi-Fi settings, static routing, and IP/MAC binding functions. D-Link’s DIR-823X series carries three command-injection vulnerabilities, all three rated critical severity, affecting the router’s DDNS, QoS, and AC-status handling functions. Critical-severity command injection is about as serious as a router vulnerability gets, since it can potentially let an attacker execute arbitrary commands on the device.
Here’s the detail worth being direct about rather than glossing over: as of the most recent tracking available, confirmed firmware patches for these specific Tenda and D-Link vulnerabilities weren’t clearly documented the way NETGEAR’s and TP-Link’s were. If you own an affected Tenda AC21, TX9, TX3, or D-Link DIR-823X unit, checking the manufacturer’s own support page directly for a firmware update, rather than assuming one already exists, is a genuinely necessary step right now, not just a routine precaution.
Why Routers Are a Worse Update Story Than Phones
It’s worth understanding why this keeps happening across so many router brands simultaneously, since it’s not really a story about any one manufacturer being careless. Smartphone operating systems push security updates through a small number of centralized channels, Apple’s and Google’s own update infrastructure, reaching most devices automatically with minimal user action required. Router firmware updates are the opposite: vendor-specific, frequently requiring a manual login to the router’s own admin interface, and inconsistent in whether automatic updates are even offered as an option, let alone enabled by default. A router that’s been quietly running in a closet for three years without ever being logged into again is an entirely normal, common setup, and it’s also a router that’s been silently accumulating unpatched vulnerabilities the entire time without anyone noticing.
How to Check Your Specific Router
A few concrete steps that apply regardless of which brand you own:
- Find the exact model number and hardware version, usually printed on a sticker on the bottom or back of the router. NETGEAR and TP-Link’s advisories are specific down to hardware version numbers (a “V4” versus “V5” of the same model name can have different vulnerability status), so the general model name alone isn’t always enough to check accurately.
- Log into the router’s admin interface directly (typically through a browser at an address like 192.168.1.1, printed on the same label as the model number) and check the current firmware version against the manufacturer’s published fixed-version list for your specific CVE.
- Enable automatic firmware updates if the router supports it, rather than relying on remembering to check manually. This is the single most effective fix for the “nobody logs into their router” problem described above.
- If you own an affected Tenda or D-Link model with no clearly published patch yet, check the manufacturer’s support page directly before assuming the problem has been handled, and consider whether the router’s affected functions (DDNS, QoS, remote management) can be disabled entirely as a temporary mitigation until a patch is confirmed available.
What an Attacker Actually Gets From These Flaws
It’s worth being concrete about what these vulnerability categories actually let someone do, since “medium severity” and “critical severity” can otherwise read as abstract labels. A command-injection flaw, the category behind D-Link’s critical-rated bugs and two of NETGEAR’s disclosures, lets an attacker who’s already on the local network, or in some cases able to intercept traffic on it, run their own commands on the router itself. From there, an attacker can potentially redirect traffic, monitor unencrypted data passing through the network, or use the router as a foothold to reach other devices connected to it, phones, laptops, smart home gear, anything sharing that same Wi-Fi network. A hardcoded-credential flaw like TP-Link’s works differently but toward a similar end: instead of exploiting a coding flaw, it hands an attacker a working login that the manufacturer never intended to be discoverable, skipping the need to guess or crack anything at all.
The buffer overflow flaws in Tenda’s lineup are somewhat narrower in most cases, generally requiring an attacker already have some level of network access before they can be exploited, but a home network with a smart TV, a few IoT devices, and a guest Wi-Fi network in regular use has more potential entry points for that initial access than most people assume, which is part of why “requires local network access” isn’t the same as “not a real risk.”
Finding Your Router’s Admin Panel
If the login address isn’t printed on the device itself, a few defaults are worth trying first before resorting to a manufacturer support search: 192.168.0.1 and 192.168.1.1 cover the large majority of home routers across all four brands discussed here, entered directly into a browser’s address bar while connected to that router’s own network. NETGEAR routers also support the friendlier `routerlogin.net` address as an alternative that works regardless of the router’s specific IP configuration. Once logged in, the firmware version is typically listed on an “Administration,” “System,” or “Advanced” settings page, the exact label varying by brand and firmware version, worth comparing directly against the specific fixed-version numbers each manufacturer’s advisory publishes for your exact model and hardware revision.
The Bottom Line
None of this means any of these four brands make categorically unsafe routers; disclosed vulnerabilities getting fixed is the security process working as intended, not evidence a brand should be avoided going forward. What it does mean is that a router bought even a year or two ago is worth actively checking against these specific 2026 advisories rather than assuming “it’s just been working fine” is the same thing as “it’s still secure.” A five-minute firmware check is a small price for closing a gap that, in D-Link’s case specifically, is currently sitting at critical severity with unclear patch availability.
*Sources: NETGEAR’s official August 2026 Security Advisory, TP-Link’s official CVE-2026-12001 advisory, SecureIoT.house’s Tenda/D-Link CVE tracking, cross-checked across multiple 2026 sources.*
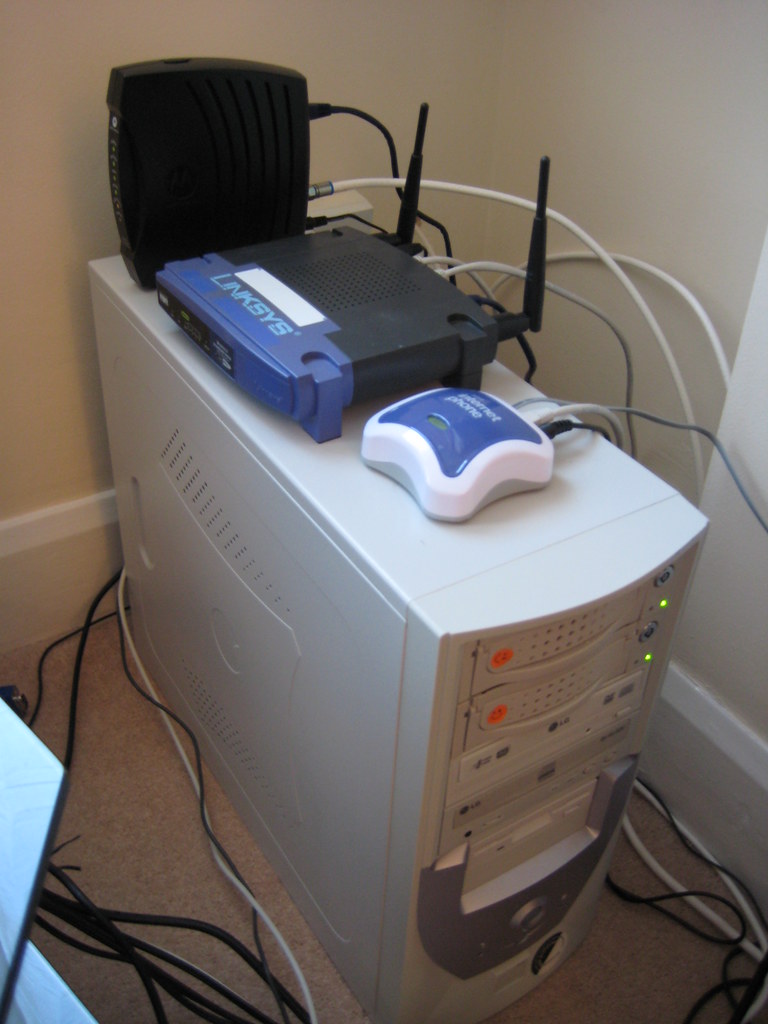
Photo credit: “home network, cable, linksys, voip, motorola” by osde8info, licensed BY-SA (https://creativecommons.org/licenses/by-sa/2.0/). Source: https://www.flickr.com/photos/8764442@N07/2562812342